Signature Management for Microsoft 365: Server-Side vs Add-In
On this page · 10 sections
TL;DR: Third-party signature tools for Microsoft 365 work in one of two ways. Server-side tools route each email through the vendor’s servers and add the signature after it is sent. Add-in tools insert the signature inside Outlook while the user writes. Microsoft’s own mail flow rules are a third, free option that works like a basic server-side tool. The choice affects your GDPR position, what employees see as they write, which devices are covered and how much IT work is involved. This article compares all three so you can ask vendors the right questions.
Most signature tools for Microsoft 365 promise the same things: central control, directory sync and a visual template editor. The feature lists look very similar.
What they do not make easy to compare is how they work. That is, what happens to an email between the sender pressing Send and the recipient getting it. Two tools with the same features can differ a lot in what they mean for your data, what employees see and which devices are covered. The architecture decides most of what follows, so it is worth settling first.
This article explains the approaches and what each one means for you. It does not recommend vendors.
The first question to ask
When IT admins compare signature tools, they usually compare features. Can it personalise per user? Does it have a visual editor? Does it support banners? How does it handle replies?
Those questions matter. But one comes first:
Does this tool add signatures by routing email through its own servers, or by inserting them inside Outlook before the email is sent?
The answer decides almost everything else about how the tool behaves and what obligations it creates.
How server-side routing works
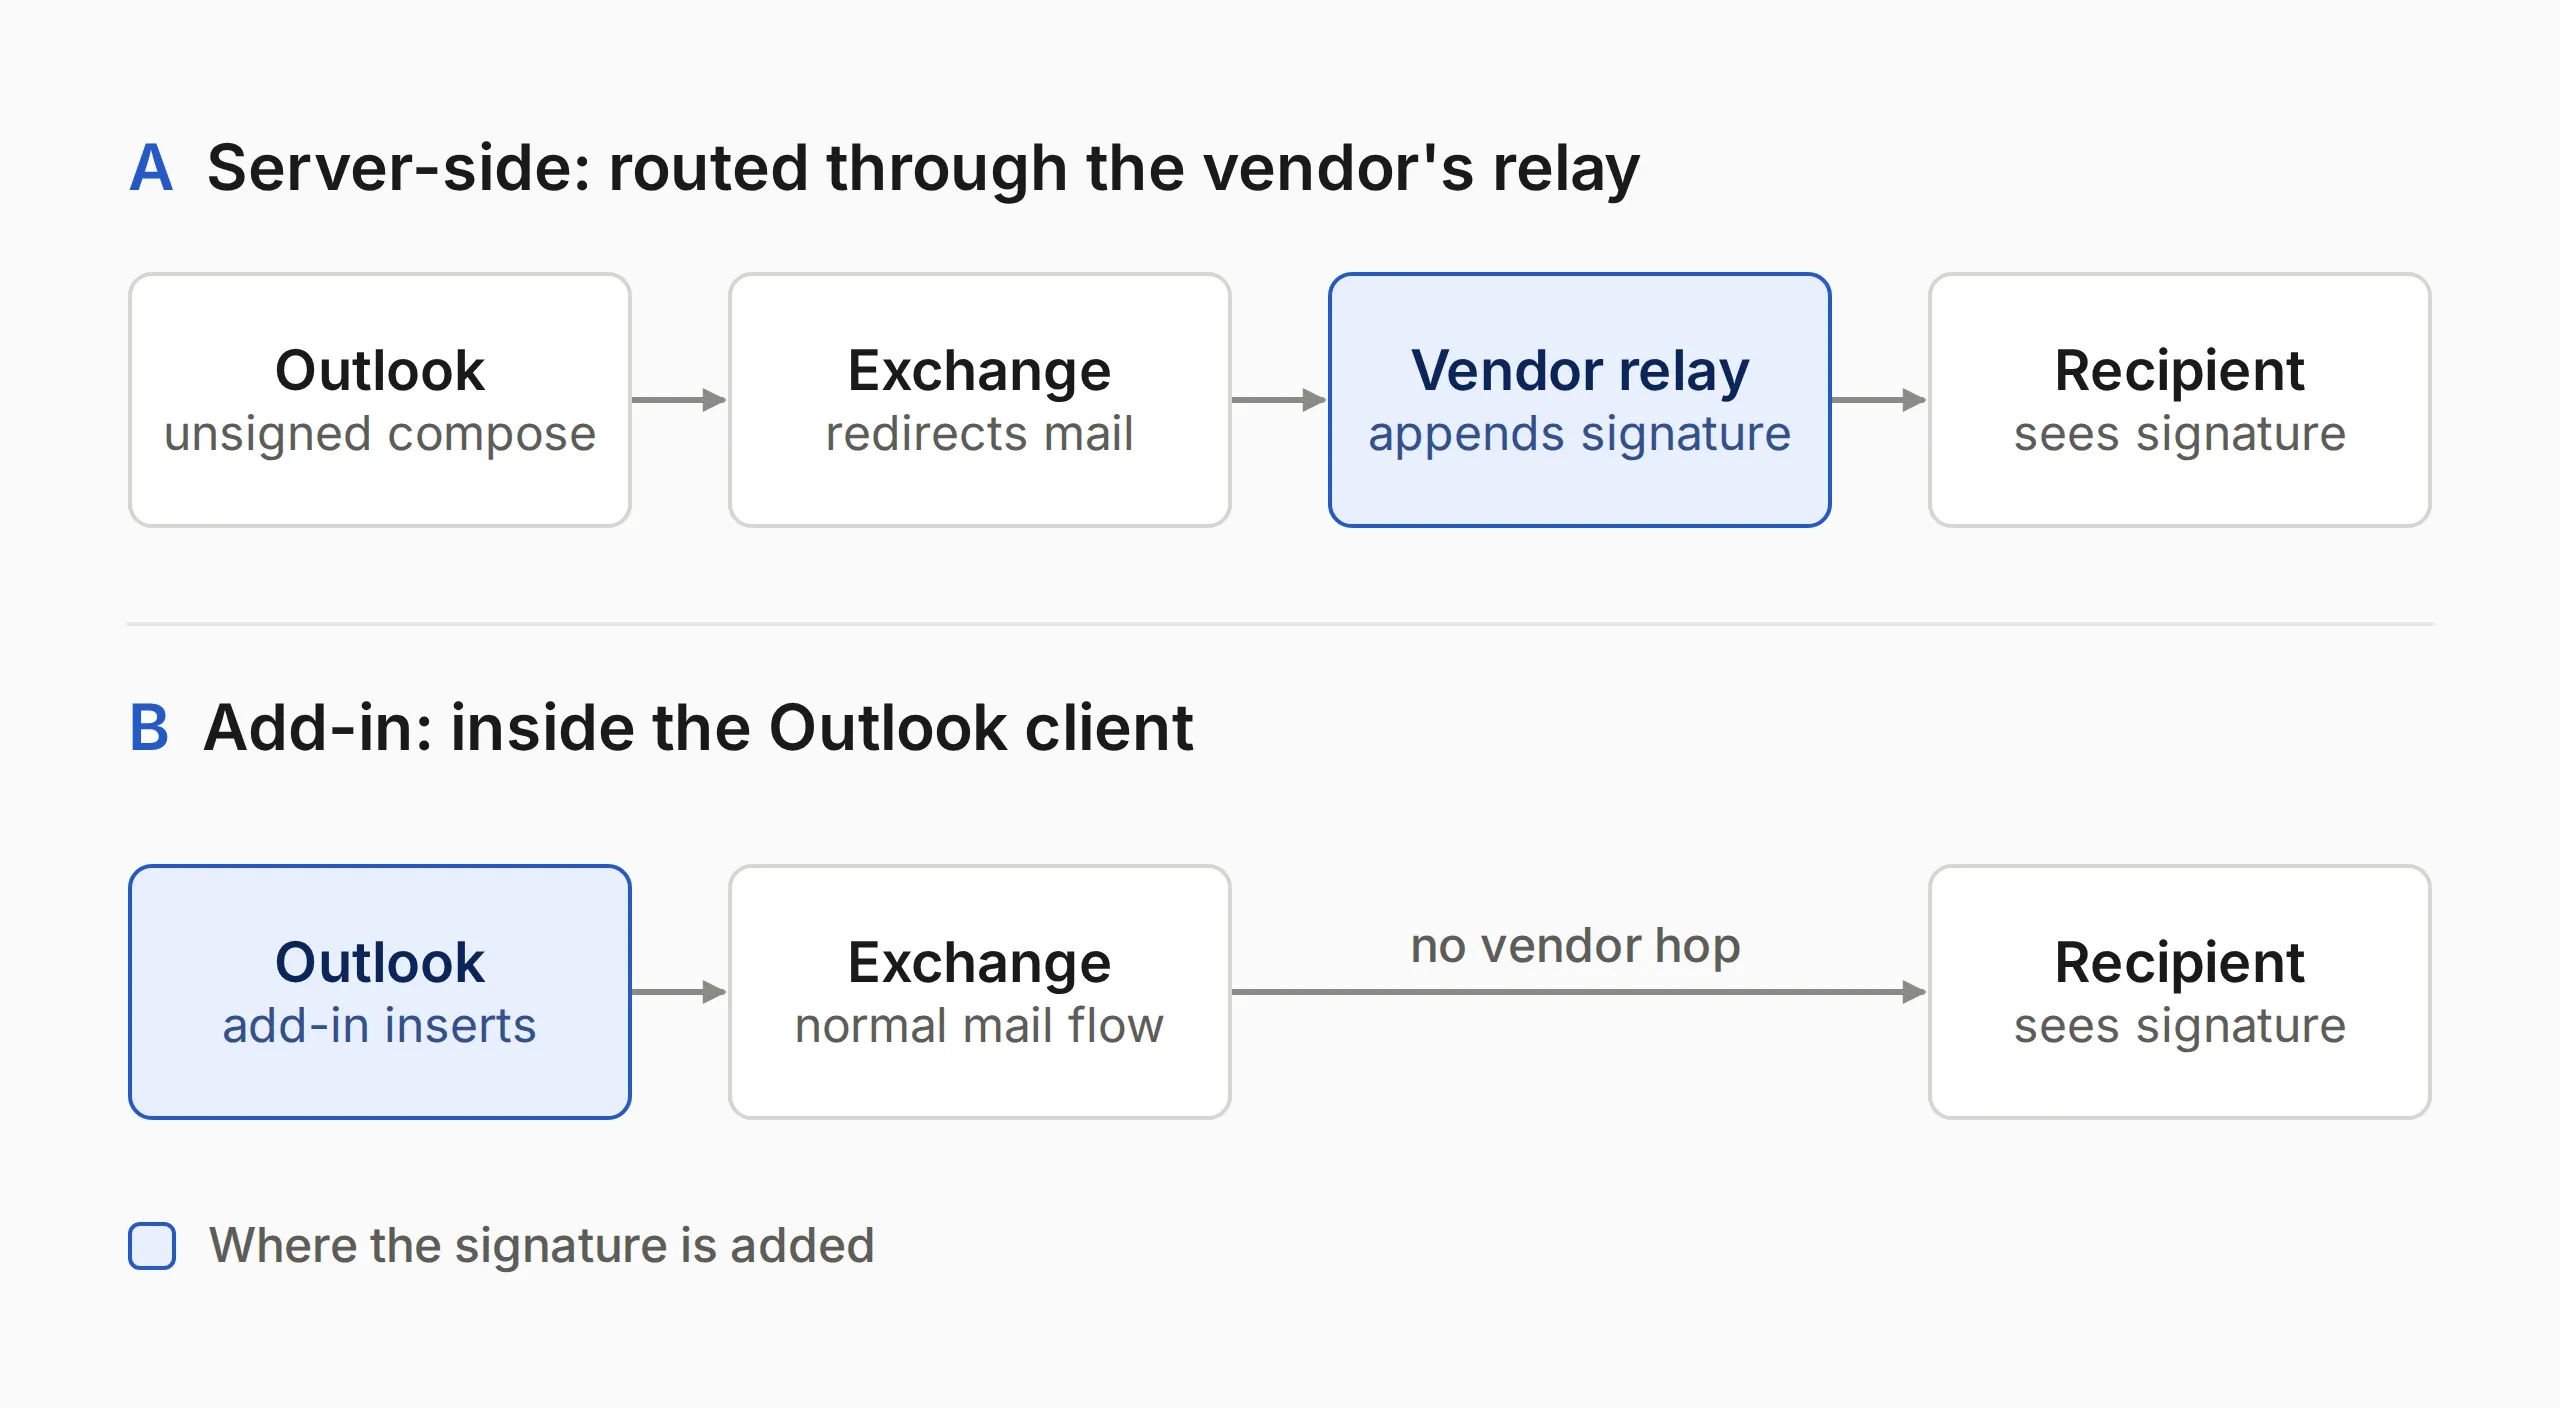
With server-side routing, your outbound email does not go straight from Microsoft 365 to the recipient. A connector in the Exchange admin centre sends it to the vendor’s cloud service first. The vendor’s servers identify the sender, look up their signature, add it to the message and send the email on.
The recipient sees a normal email with a branded signature. But every email your organisation sends has passed through a third party on the way.
Many of the large, established vendors use this approach. It works, and for many organisations it is a reasonable choice.
What the employee sees: nothing. They write an email and press Send. The compose window shows no managed signature, or only one they set up themselves. The managed signature is added in transit, so the sender never sees it.
That causes a recurring problem. Employees do not know the signature is there, so some add their own as well, and recipients get two. Employees also cannot check their signature without sending themselves a test email.
What it means for IT: you set up a connector so outbound mail goes through the vendor’s relay (a mail server that passes messages on). That is not hard to do, but your outbound mail now depends on the vendor’s service. If the relay goes down, delivery can be affected. Most vendors have a fallback, so mail is delivered without a signature rather than not at all. Ask what theirs is.
How add-in injection works
With an add-in, a small piece of software, an Outlook add-in, runs inside Outlook. IT deploys it to everyone from the Microsoft 365 admin centre. It starts automatically when an employee opens a new email.
The add-in identifies the sender, fetches their signature (usually a ready-made HTML file the vendor keeps on a content delivery network) and puts it into the email. The email is then sent the normal way: Outlook, then Exchange Online, then the recipient. The vendor plays no part in delivering it.
What the employee sees: their signature, already in place when they open a new email, looking as it will to the recipient. There is no reason to add their own, so duplicates mostly disappear. Employees can also spot a wrong job title or an old banner and report it before it goes out.
What it means for IT: you deploy the add-in once, to everyone or to chosen groups, with Microsoft’s Centralised Deployment. You do not touch individual machines. Microsoft says a new deployment can take up to 24 hours to reach all users, and later changes up to 72 hours. There is no connector to set up and nothing added to your mail flow. For a step-by-step walkthrough of Centralised Deployment, including the permissions and screens involved, see Centralised Email Signature Management in Microsoft 365.
The free option: Microsoft’s mail flow rules
Microsoft 365 can add a signature or disclaimer itself, using Exchange mail flow rules (also called transport rules). Like a server-side tool, a rule works on the mail server after the email is sent, but the email never leaves Microsoft.
A rule can fill in each sender’s name, job title and phone number from the directory. It cannot vary the design by person or team, show the signature while someone writes, or place it neatly above quoted text in a reply. It suits a legal disclaimer. It rarely suits a branded signature. The complete guide covers what mail flow rules can and cannot do in detail, with screenshots.
Five practical differences
1. What employees see while writing
Server-side: the managed signature is invisible until the recipient gets the email.
Add-in: the signature is there from the moment the compose window opens.
This is the difference people notice most day to day. If you use several signature variants, or banners that change by campaign, an add-in means employees always know which one is active. With server-side routing they cannot.
2. What the vendor’s systems see
This is the most important difference if you are under UK or EU GDPR.
Server-side: every outbound email, including the body, attachments and recipients, passes through the vendor. That makes the vendor a data processor of your email content under Article 28 of the UK GDPR. You need a Data Processing Agreement (DPA) that covers it.
Add-in: the email does not pass through the vendor. A well-built add-in only fetches a signature file. It does need a permission that also lets it read the message, so whether anything else is sent is a fact about the vendor’s code, which you should check. You still need a DPA, but a much narrower one, covering employee profile data.
A quick test works on any vendor: ask, “Does email content pass through your servers?” A clear answer tells you the architecture, whatever the marketing pages call it.
What each architecture sends, what Article 28 requires in the DPA, how to check an add-in and the full list of vendor questions are all in Email Signature Tools and GDPR: What Your DPO Needs to Know.
3. Mobile coverage
This is where server-side routing has a real advantage.
Server-side: the signature is added on the mail server, so it works whatever app sent the email. That includes the Outlook mobile app and native apps such as iOS Mail.
Add-in: it works in Outlook on Windows, Mac and the web. It reaches the Outlook mobile app only if the vendor has built Microsoft’s mobile support for signature add-ins, which takes extra work and which many tools do not have. No add-in can reach a native mail app such as iOS Mail or Gmail.
So the add-in approach suits organisations where people send from Outlook on managed devices. If many staff send from personal phones with native mail apps, server-side routing covers them more reliably. Ask the vendor, then test it. Why Your Email Signature Does Not Show Up on Mobile explains the detail and gives a test to run on any tool.
4. Set-up and ongoing IT work
Server-side: you configure a connector once, but the vendor’s relay stays in your outbound mail path. Changes to it, or to the vendor’s infrastructure, may need IT time.
Add-in: once deployed, the add-in reaches assigned users without further work. There is nothing in the mail flow to maintain. Template changes are made in the vendor’s admin portal, usually by marketing or comms, without IT. Vendor updates to the add-in load automatically.
With either type, template changes should not need an IT ticket.
5. Sent Items
Server-side: the signature is added after the email leaves the mailbox, so by default the copy in Sent Items has no signature. Microsoft’s own documentation says this about its mail flow rules, and the same mechanism applies to a third-party relay. Exclaimer and CodeTwo both offer a fix that copies the signed version back into Sent Items afterwards (checked October 2026):
- CodeTwo’s Sent Items Update works only in its cloud or combo mode, and must be registered in your tenant.
- Exclaimer offers a Sent Items update too. Its support site notes that it may not work in classic Outlook when Cached Exchange Mode is on.
Ask any vendor whether it offers one, and test it with your Outlook set-up.
This matters most where compliance teams need Sent Items to show exactly what was delivered, as in some regulated financial firms.
Add-in: the signature is in the email before Send is pressed, so the Sent Items copy has it. What you see is what the recipient got.
The three approaches compared
| Native mail flow rules | Server-side tool | Add-in tool | |
|---|---|---|---|
| Cost | Included with Microsoft 365 | Per user per month | Per user per month |
| Per-user personalisation | Basic: directory tokens in one fixed layout | Yes, from directory sync | Yes, from directory sync |
| Signature visible while writing | No | No | Yes |
| Email content passes through a third party | No | Yes, every message | No |
| Data processing relationship | Microsoft only | Broad DPA with vendor | Narrow DPA with vendor |
| Outlook mobile app | Yes | Yes | Only if the vendor built mobile support |
| Native mobile mail apps | Yes | Yes | No |
| Signature in Sent Items | No | Not by default; CodeTwo and Exclaimer offer an update, with conditions | Yes |
| Visual template editor | No (raw HTML) | Yes | Yes |
| Reply and forward control | Limited | Yes | Yes |
| Deployment | Exchange admin centre | Exchange connector | Centralised Deployment |
| Adds a dependency to mail flow | No | Yes, the vendor’s relay | No |
| Best fit | A basic legal disclaimer | Mixed devices, personal phones, native mail apps | Managed devices using Outlook; privacy-sensitive organisations |
Which approach fits your organisation?
It depends mostly on two things: which devices and apps people send from, and how sensitive your email content is.
- Managed devices, with Outlook as the email app everywhere: the add-in approach covers you and gives the simpler data position. There is little reason to route email through a third party.
- Personal devices and a mix of mail apps, where mobile coverage is a must: server-side routing is more reliable. Treat the GDPR side as a managed obligation: get the DPA in place and know what the vendor keeps and for how long.
- A regulated sector, such as financial services, healthcare or legal: the add-in approach’s narrower data footprint is often the argument your DPO finds most persuasive.
- Only a legal disclaimer needed: native mail flow rules are free and add no new vendor.
Neither third-party approach is better in every case. Both are used successfully by large organisations. The question is which trade-offs fit yours.
Vendors that offer both modes
Some vendors offer a server-side mode and an add-in mode, in different plans or as settings in one product. That sounds like the best of both, but it brings a different risk. If both are active, an email can get two signatures: one from the add-in while writing, and one from the relay in transit.
If a vendor offers both, ask exactly how it prevents double signatures. Ask what happens to an email that the add-in has already signed when it then passes through the relay. The answer should be specific and something you can test.
Summary
The most useful question to ask any signature vendor is: “Does email content pass through your servers?”
Server-side tools route outbound email through the vendor. They cover every mail app, including native mobile apps, but the vendor processes your email content and employees never see the signature while writing.
Add-in tools insert the signature inside Outlook. The email does not pass through the vendor, and employees see their signature as they write. The limits are mobile: native mail apps are never covered, and the Outlook mobile app only if the vendor has built for it.
Once you know which category fits, the feature lists get much easier to compare. The question matters most for enterprise and compliance-led platforms. See the three types of email signature software for how that tier differs from simple generators and marketing-led platforms.
Frequently asked questions
Do vendors use different names for these two architectures?
Yes. There is no standard term, so it helps to know the aliases when you compare vendor sites. Exclaimer’s product pages call server-side delivery “cloud deployment” and add-in or client-side delivery “device deployment”. CodeTwo calls its server-side option “cloud (server-side)” signature mode and its add-in option “Outlook mode”. Rocketseed talks about “cloud, on-premises, or hybrid” deployment. That is a related but separate question: where the vendor’s own infrastructure is hosted, not whether your email routes through it. Whatever the name, ask whether your email content passes through a third party’s servers.
What is an Outlook add-in, and how is it different from a COM add-in?
A modern Outlook add-in is a small web app, built with HTML, CSS and JavaScript, that runs inside Outlook. The same add-in works in new Outlook for Windows, Outlook for Mac and Outlook on the web. A COM add-in (also called a VSTO add-in) is older, compiled Windows code. It only works in classic Outlook for Windows and does not run in new Outlook. Modern signature tools use the web-based model. New Outlook for Windows and email signatures explains what that means for the move between the two.
Does server-side routing affect email delivery reliability?
It adds a dependency, because outbound email passes through the vendor’s relay. Reputable vendors build for high availability and publish uptime commitments. If the relay fails, most deliver the email without a signature rather than holding it. Ask about the vendor’s fallback behaviour and service level before you commit.